

Three proposals land on your desk. One offers SOC as a Service. One offers managed security services. The third offers managed security operations. All three mention 24/7, all three mention analysts, and the prices are nowhere near each other. It is a common place to get stuck, and a costly one if you sign for the wrong thing.
The labels overlap because the market uses them loosely. What matters is not the name on the proposal but four practical questions: what is being watched, who investigates, who is allowed to act, and what you receive as evidence afterwards.
The short answer
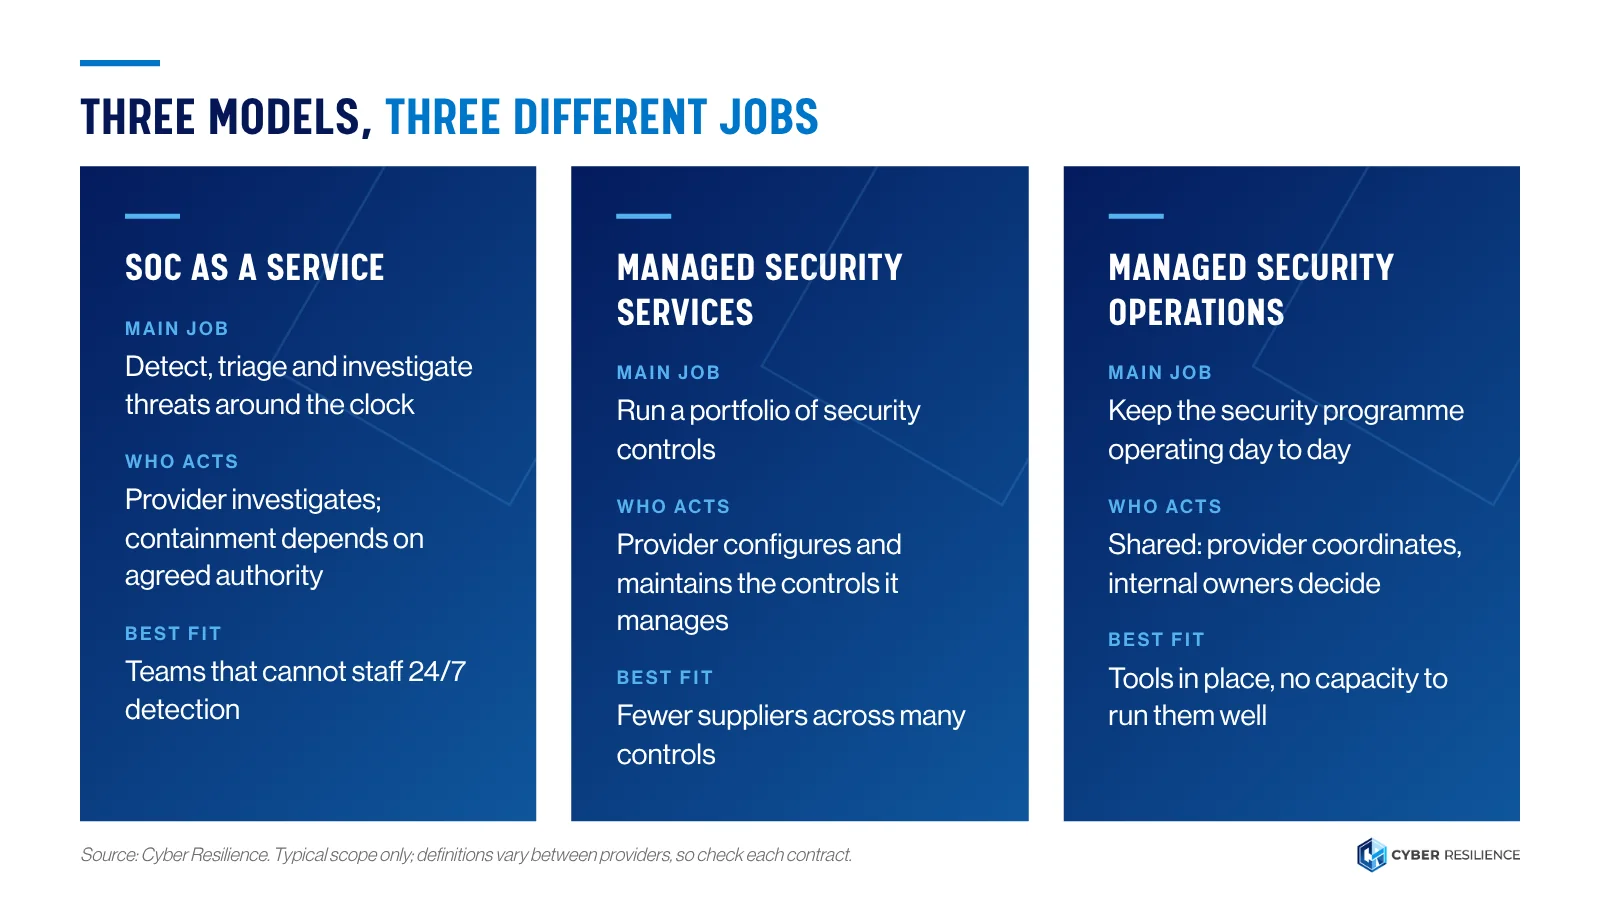
SOC as a Service gives you a Security Operations Centre (SOC) that monitors, triages and investigates security alerts on your behalf. Managed security services are a broader bundle that can include SOC monitoring plus firewall, vulnerability and endpoint management. Managed security operations is the operating layer that coordinates those activities alongside your own team.
What each term usually means
Definitions vary between providers, so treat the descriptions below as the typical scope, then check the contract for the real one.
SOC as a Service (SOCaaS)
A specialist team monitors security telemetry (log and event data from your identities, endpoints, servers, cloud platforms and network) and works through the alerts. Tier 1 analysts triage, Tier 2 analysts investigate, and confirmed threats are escalated or contained according to the authority you have agreed. Managed detection and response (MDR) sits close to this: MDR usually leans more heavily on endpoint detection and includes pre-agreed response actions such as isolating a device. See how we describe our SOC as a Service and managed detection and response scope.
Managed security services (MSS)
A provider runs several security capabilities for you over time. Monitoring may be one of them, but the bundle often includes firewall management, vulnerability scanning and patch oversight, endpoint protection, threat intelligence and periodic advisory. Organisations that buy from a managed security service provider (MSSP) are usually buying breadth: fewer suppliers and one point of accountability across several controls. Our managed security services page sets out a typical scope.
Managed security operations
This is the day-to-day operating layer that keeps the security programme moving: alert triage and escalation, remediation follow-up, vulnerability and identity hygiene, reporting and the coordination between IT, security and suppliers. It is often co-managed, meaning your internal team keeps decision-making and business context while the provider supplies capacity and specialist skill. See managed security operations.
Side by side: how the three models compare
| SOC as a Service | Managed security services | Managed security operations | |
|---|---|---|---|
| Main job | Detect, triage and investigate threats around the clock | Run a portfolio of security controls | Keep the security programme operating day to day |
| What is watched | Telemetry from agreed sources (identity, endpoint, network, cloud) | The controls in scope, e.g. firewall, endpoints, scanning | Alerts, open findings, remediation and reporting across teams |
| Who acts | Provider investigates; containment depends on agreed authority | Provider configures and maintains the controls it manages | Shared: provider coordinates, internal owners decide |
| Typical evidence | Case notes, escalations, detection coverage, monthly reports | Change logs, patch and scan status, service reviews | Remediation tracking, risk reporting, management reviews |
| Best fit | Teams that cannot staff a 24/7 detection capability | Organisations wanting fewer suppliers across many controls | Organisations with tools in place but no capacity to run them well |
| Watch out for | "24/7" that means monitoring, not response | Broad scope with thin monitoring depth | Unclear ownership of fixes |
Why the difference matters at 02:00
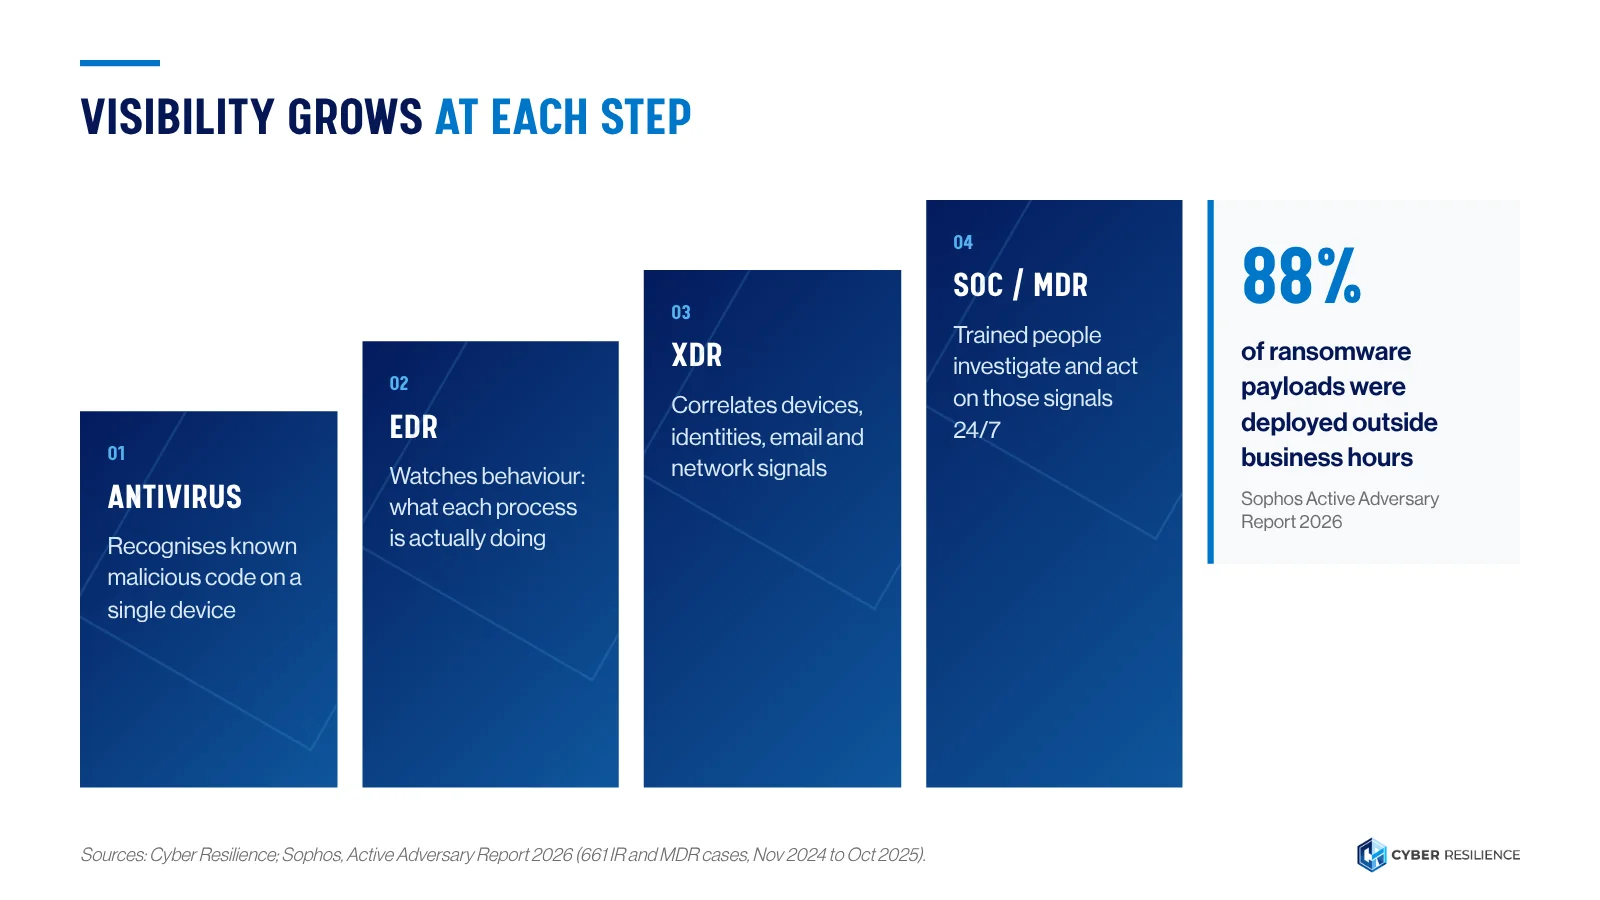
The distinction stops being academic outside office hours. Sophos’s 2026 Active Adversary Report, based on 661 incident response and MDR cases, found that 88% of ransomware payloads were deployed outside business hours and that attackers reached Active Directory a median of 3.4 hours after getting in. Mandiant’s M-Trends 2026 reports that the median time between initial access and the hand-off to a second criminal group fell to 22 seconds in 2025.
“Attackers do their homework during the day. They watch how you work, then act when they expect nobody to be looking. If your IT people work office hours, the real question is who responds when it happens at midnight.”
Qurash Ramlal, Customer Success Manager, Cyber Resilience
If you bought monitoring without response authority, the provider may see the attack at 02:00 and send an email that someone reads at 07:30. If you bought a managed firewall without monitoring, nobody may be looking at all. Neither is a failure of the provider; it is a gap in what was bought. Our earlier article on who is investigating your security alerts at 02:00 covers this in more depth.
Visibility is what you are really paying for
Most organisations climb the same ladder. It starts with antivirus on each device, which recognises known malicious code. Endpoint detection and response (EDR) adds behaviour: what a process is actually doing. Extended detection and response (XDR) correlates signals across devices, identities, email and the network, so an attack spotted on one laptop can be stopped before it reaches the next. A SOC or MDR service then puts trained people behind those signals, every hour of the day.
“The difference between a low-cost setup and a properly managed environment is visibility and governance: seeing what is happening across the estate, and knowing how well it is being controlled.”
Qurash Ramlal, Customer Success Manager, Cyber Resilience
Technology alone does not close the gap. In the same interview Qurash put it simply: the team is what makes the tools work. A SOC that receives alerts nobody has tuned, or that cannot see your identity platform, is watching the wrong things very carefully.
Which model fits which business?
- You have good tools but nobody watches them overnight. SOC as a Service or MDR is the natural fit. Start with the systems whose compromise would hurt most.
- You want fewer suppliers and one accountable partner. Managed security services, provided the monitoring component is specified as tightly as the rest.
- You have a capable IT team that is stretched. Managed security operations on a co-managed basis keeps your people in control while adding capacity for triage, remediation follow-up and reporting.
- You are regulated and need evidence. Whichever model you choose, insist on case records and reporting that an auditor or the Information Regulator could follow. Financial institutions should map the service to Joint Standard 2 of 2024, which has applied since 1 June 2025.
Many organisations end up with a combination: SOC as a Service for detection, plus managed operations for the remediation work that detection uncovers. If you are weighing an internal build instead, read SOC as a Service vs an in-house SOC.
Six questions that reveal what a proposal really includes
- Which identities, systems, cloud platforms and log sources are in scope on day one, and which are excluded?
- Are analysts on shift 24/7/365, or is it the tooling that runs 24/7?
- What can the provider do without phoning you first: disable an account, isolate a device, block an address?
- Who owns the fix once a vulnerability or misconfiguration is found, and how is it tracked to closure?
- What will the monthly report show beyond alert counts: detection coverage, response times, recurring causes?
- Where is your telemetry stored and processed, who can access it, and how does that align with POPIA?
Common mistakes when comparing proposals
- Comparing prices before scope. A cheaper monitoring service that excludes identity or cloud logs is not cheaper; it is smaller.
- Assuming “24/7” includes response. Ask for the escalation matrix and the list of pre-authorised actions.
- Buying monitoring without remediation capacity. Detection that produces findings nobody fixes simply documents risk.
- Forgetting third parties. If a supplier manages your firewall or remote access, make sure its activity is in the monitoring scope. Verizon’s 2026 Data Breach Investigations Report found third-party involvement in 48% of breaches.
Where Cyber Resilience fits
Cyber Resilience offers all three models and scopes them to the environment rather than the label: SOC as a Service for detection and investigation, managed security services where a broader portfolio makes sense, and managed security operations alongside internal teams. Because the practice began in digital forensics, investigations are documented with the evidence trail a board, insurer or regulator may later ask for.
Next step: Book a scoping call. Bring a list of your security tools, your critical systems and your current escalation process, and we will map which model fits.
Key takeaways
- SOC as a Service detects and investigates; managed security services run a portfolio of controls; managed security operations keeps the programme moving day to day.
- Compare scope, response authority and evidence before you compare price.
- Most ransomware is deployed outside business hours, so confirm who acts at night, not just who watches.