
The short answer
SOC as a Service provides a defined security monitoring and investigation capability without requiring an organisation to staff every specialist function internally. The right approach depends on the systems at risk, the required coverage and who can act when an incident occurs.
The alert your business might not see until morning
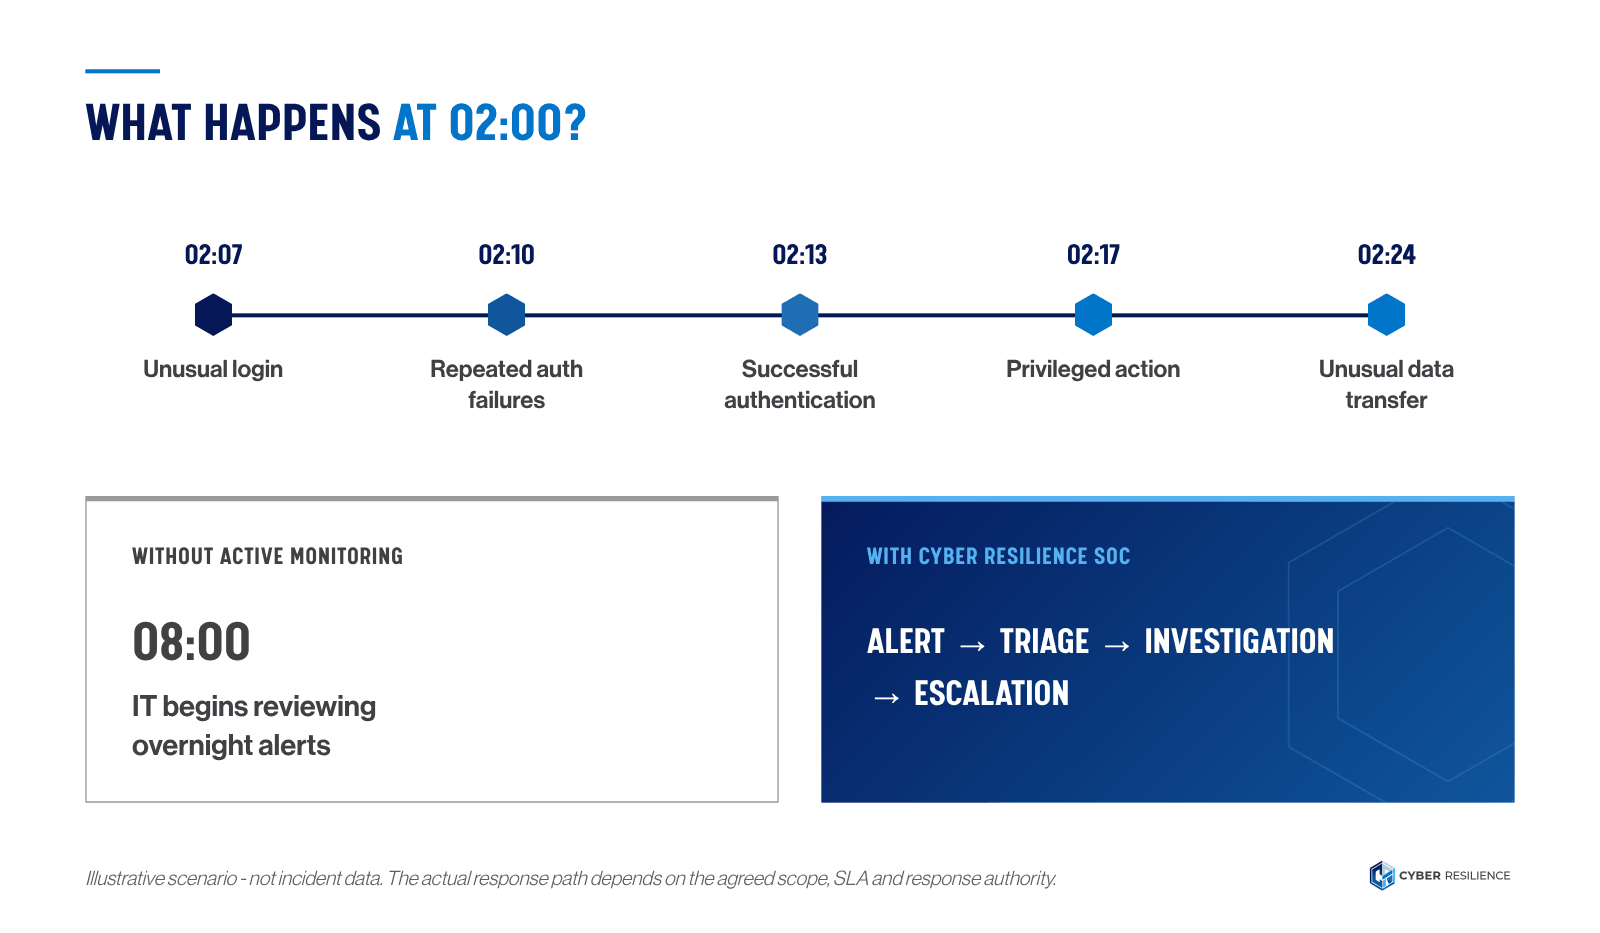
At 02:07, an employee account signs in from an unusual location. A few minutes later, repeated authentication attempts occur. Then a privileged action, followed by an unexpected data transfer. Each event might generate its own notification. The question is whether anyone is awake to connect them.
This is an illustrative scenario, not a Cyber Resilience client incident. But it captures a real operational problem: buying security tools does not guarantee that suspicious activity will be investigated when it happens.
What is SOC as a Service?
SOC as a Service (SOCaaS) gives a business access to a managed security operations capability. Depending on the contract, a specialist team monitors security signals, separates harmless activity from potential threats, investigates incidents and escalates findings to the people authorised to act.
It is not simply another alerting tool. The value lies in context: recognising that a login, a device event and a cloud action may be part of the same story.
Why after-hours coverage matters
Security threats do not wait for the working day. CrowdStrike’s 2026 report describes an average eCrime breakout time of 29 minutes in its 2025 observations. That is not the average time to detect an attack, but it illustrates how quickly an attacker can move after initial access.
A system may detect suspicious activity in seconds. If nobody investigates until the next morning, that early warning may not translate into a timely response. For a business, the practical question is simple: who owns the next step?
What happens after an alert?
A well-defined SOC workflow takes an event through initial triage, classification, deeper investigation where necessary and escalation or response. Some alerts are false positives. Others require context from identities, endpoints, servers or cloud services before their significance becomes clear.
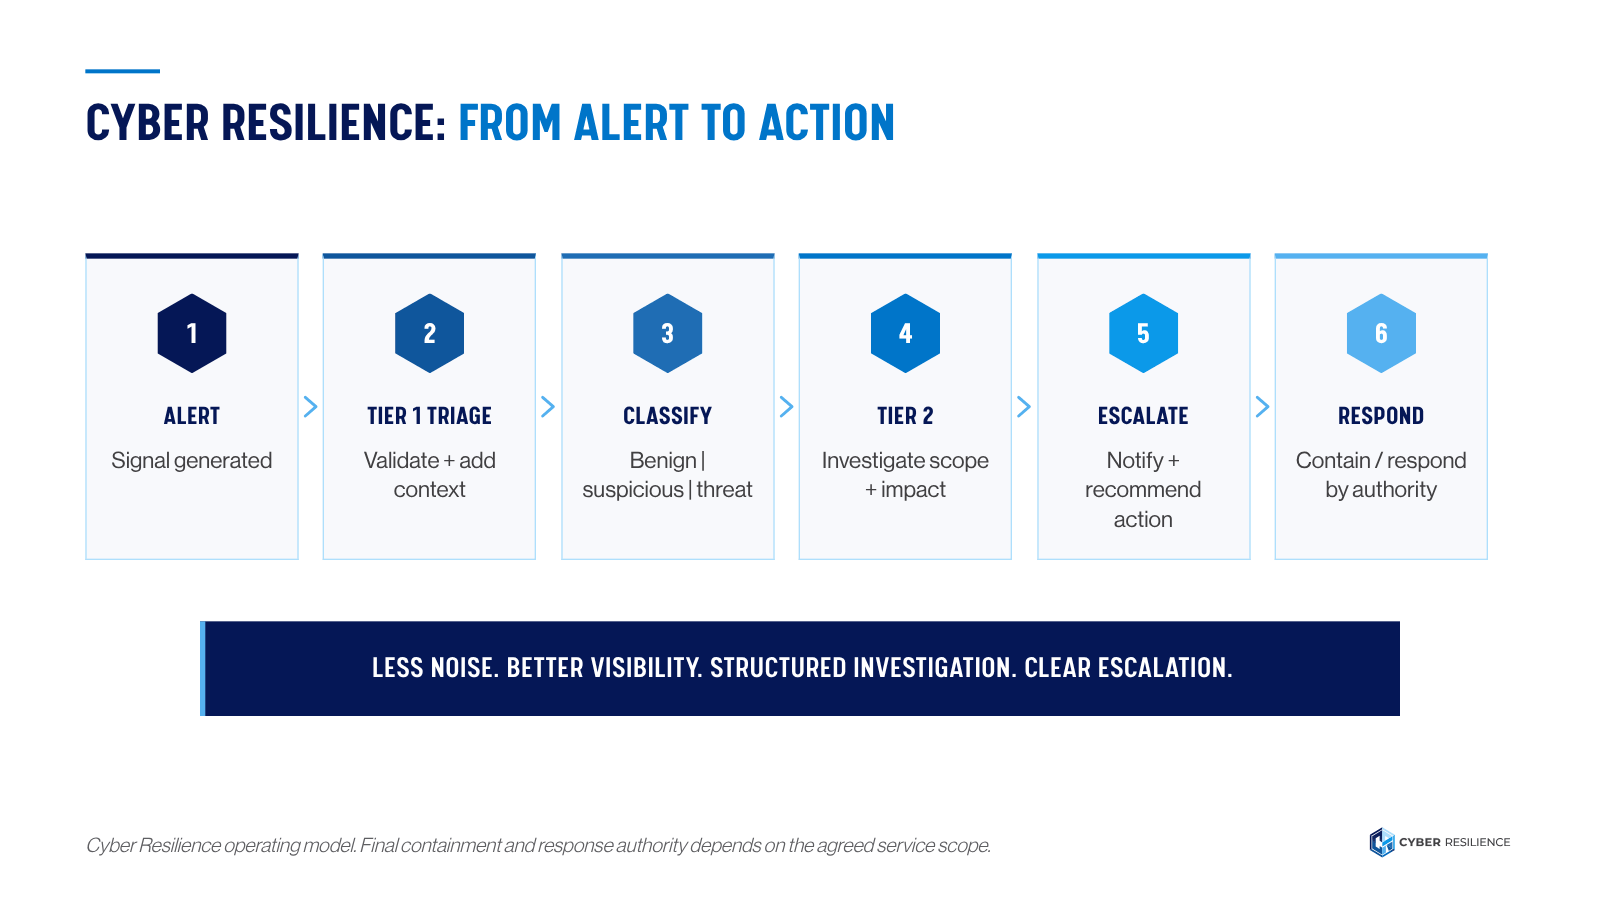
Cyber Resilience describes its operating model around Tier 1 triage, classification, Tier 2 investigation and clear escalation. What happens next depends on agreed responsibilities: the SOC may notify the customer, recommend containment or take pre-authorised actions.
Five signs it is time to review your security operations
- Your tools send alerts, but nobody routinely investigates them outside business hours.
- Your IT team is expected to handle incidents without dedicated investigation capacity.
- You cannot easily connect activity across identity, endpoints, networks and cloud systems.
- You are unsure who can isolate a device or disable an account during an incident.
- Management sees alert totals but cannot tell whether detection and response are improving.
None of these signs automatically mean you need a fully outsourced SOC. They do mean it is worth reviewing the gap between your current controls and the capability your business expects.
Does this mean replacing your internal IT team?
Not necessarily. A co-managed SOC can complement capable internal teams. Your people keep business context and decision-making authority while an external specialist provides monitoring, after-hours triage or investigation support.
For some organisations, a mature in-house SOC is the right answer. The decision should follow the required level of coverage, risk, internal skills and the capacity to sustain the service—not a sales pitch for one operating model.
What should you expect from a provider?
Ask what systems are actually monitored, which integrations are included, whether qualified analysts provide the contracted coverage, how fast high-priority alerts are investigated, who receives escalations and what the provider is authorised to do.
Request an example of an incident report. A useful report explains what happened, what was affected, what action was taken or recommended, and what should improve next. If the service mainly forwards raw alerts, it may not be solving your team’s biggest problem.
The most important question
Your business may already be generating the right signals. The missing capability could be someone with the time, tools and judgement to understand them—and a clear route to action.
Cyber Resilience can help you review your monitoring coverage, investigation arrangements, and response responsibilities, then explore whether an outsourced, co-managed, or internal approach best fits your environment.
Next step: Talk to the Cyber Resilience Security Operations team about your current coverage and the gaps you want to close.
Key Takeaways
- Security tools generating alerts are not the same as an actively operated SOC.
- After-hours monitoring is useful only when alerts are investigated and escalated.
- An internal, outsourced or co-managed model can work if responsibilities and response authority are clear.
How Cyber Resilience Can Help
Cyber Resilience can help your organisation review monitoring visibility, investigation responsibilities and the operating model best suited to its environment. Speak to the Security Operations team to discuss the next practical step.